For Bank of Ghana regulated institutions. This is Goldline's Ghana practice, distinct from our UK programmes.
BoG CISD compliance and ISO 27001 certification, delivered as one programme.
For Ghanaian banks, specialised deposit-taking institutions, savings and loans companies, and payment service providers required to comply with the Bank of Ghana Cyber and Information Security Directive. Regulatory compliance and internationally recognised certification in a single engagement.
Fixed-fee project. Senior practitioner-led. Local partner in-market.
Delivered by
45 minute call. No sales pitch. Senior practitioner-led discovery.
Loading the calendar
Open the booking pageCalendar not loading? Open Calendly directly
Calendar not loading? Open Calendly directly
info@goldlineconsultancy.co.ukBoG CISD is not optional best practice. It is a regulatory obligation with supervisory teeth.
Mandatory scope
Over 100 licensed institutions in scope across banks, specialised deposit-taking institutions, savings and loans companies, and payment service providers.
Supervisory enforcement
The Bank of Ghana enforces CISD compliance through its existing supervisory framework. Non-compliance carries regulatory consequences.
Five domains of obligation
Information security governance, risk management, incident management, third-party risk, and business continuity.
Direct mapping to ISO 27001
CISD requirements map onto ISO 27001 Annex A controls with substantial overlap. A single engagement satisfies both.
International partner pressure
International correspondent banks and payment networks increasingly require ISO 27001 from Ghanaian counterparties. CISD plus ISO 27001 unlocks both regulatory and commercial pathways.
Regulatory compliance and international certification, built once.
Most Ghanaian financial institutions facing CISD compliance and international partner pressure treat them as two separate programmes: one for the regulator, one for the international counterparty. The Goldline approach inverts this. CISD and ISO 27001 share a substantial control set. Implementing the two regimes through a single engagement is materially more efficient than running them in parallel or in sequence.
- Single engagement satisfies BoG CISD supervisory expectations
- Same engagement delivers ISO 27001 certification recognised internationally
- Existing CISD requirements substantially reuse into the ISMS
- International contracts unlock without a second compliance programme
What the BoG CISD 2026 Programme covers.
Fixed-fee project. Senior practitioner-led delivery. Local partner in-market for relationship continuity.
- ISMS scope and Statement of Applicability aligned to CISD requirements
- CISD gap analysis against current operating state
- Information security governance framework
- Risk management methodology and risk register
- Incident management procedures including BoG notification templates
- Third-party risk management programme
- Business continuity and disaster recovery alignment
- Policy framework drafted to BoG audit standard, tailored to your operating environment
- Internal audit and audit-grade evidence pack
- UKAS-accredited ISO 27001 certification body coordination (for the certification track)
- Senior practitioner-led delivery, with local partner in-market support
Fixed-fee project. Pricing for the engagement is discussed directly on the scoping call and reflects the institution's size, scope, and current CISD maturity.
Who delivers this
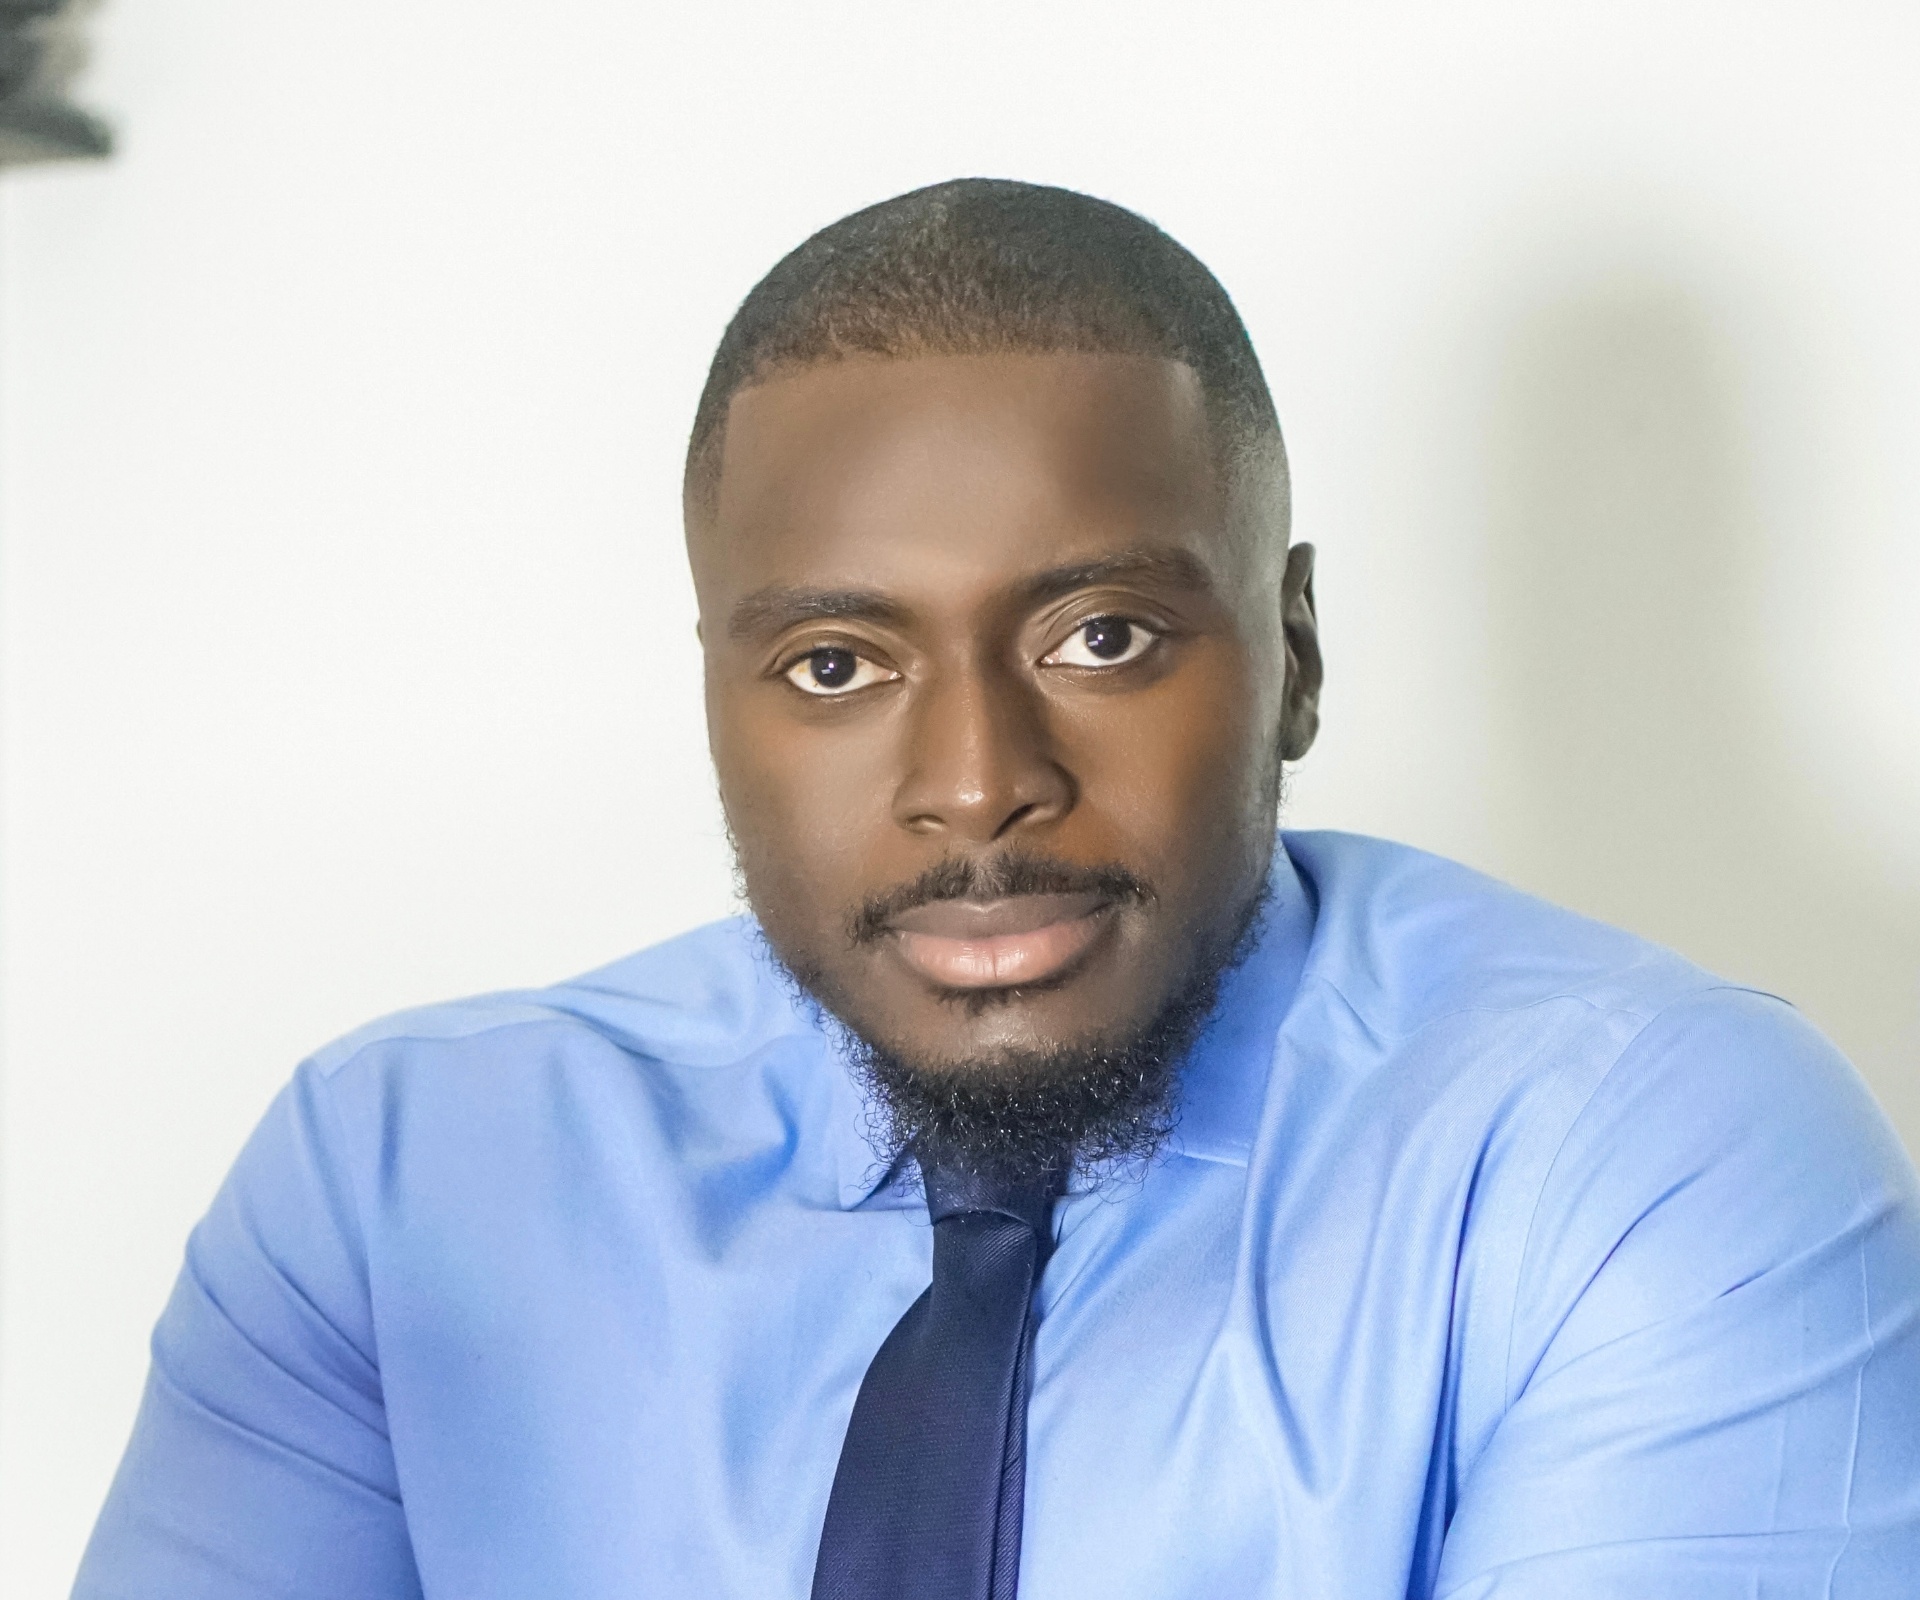
Alfred Obeng
Founder and Principal Consultant, Goldline Consultancy
Senior practitioner with thirteen years across UK Defence, Central Government, Automotive, Big Tech, and Regulated Industries. ISO 42001 Lead Implementer (PECB), ISO 42001 Lead Auditor (PECB), ISO 27001 Senior Lead Implementer (PECB), ISO 27001 Lead Auditor (PECB), CISSP, PMP. Currently reading an Executive MBA with AI specialism at the University of Hertfordshire.
BoG CISD compliance is enforced through Ghana's banking supervisory framework. The cost of getting it wrong is regulatory, not just commercial. Senior practitioner-led delivery, with local partner in-market for relationship continuity, is the operating model designed for that.
From the first conversation to the certificate, the practitioner you meet is the practitioner doing the work. With local partner support in-market for relationship continuity.
Questions buyers ask before scoping.
Ready to scope your CISD programme?
Book a 45 minute strategy call. Senior practitioner-led discovery. No commitment to scope on the call.
Or email Alfred directly: info@goldlineconsultancy.co.uk