
Defence supply chain · DCC Level 0
DCC Level 0 by 31 December 2026.
The Ministry of Defence expects its industry partners to hold Defence Cyber Certification at Level 0 as a minimum. Goldline prepares UK defence suppliers to meet it.
Readiness, implementation, and evidence preparation. Certification is issued by an IASME-accredited Certification Body, not by Goldline.
Loading the calendar
Open the booking pageCalendar not loading? Open Calendly directly
What the requirement actually is
Defence Cyber Certification is the MOD supply chain assurance scheme, operated by IASME on behalf of the Ministry of Defence and assessed against Def Stan 05-138 Issue 4. It replaces self-declared cyber posture with independent assessment.
The MOD has set an expectation that defence industry partners hold DCC at Level 0 as a minimum by 31 December 2026. Suppliers on contracts carrying a higher Def Stan 05-138 risk profile are expected at Level 1 or above.
It is an expectation rather than a legal requirement. IASME's own FAQ still states that DCC is not mandatory. Contractual force arrives through DEFCON 658 and the Cyber Risk Profile attached to a specific contract.
For most SMEs the practical trigger arrives earlier than the deadline, through a Tier 1 prime asking for evidence during re-tender or supplier review.
The four DCC levels
The level in scope follows the Def Stan 05-138 risk profile of the contracts you hold, not the size of your organisation.
Level 0
Foundational cyber hygiene, evidenced by a valid Cyber Essentials certificate and a small set of baseline controls. The tier the MOD expects across the defence industry base by 31 December 2026.
Level 1
One hundred and one controls across five objectives covering governance, asset management, access control, and supplier security. Applied where the Def Stan 05-138 risk profile is moderate.
Level 2
One hundred and thirty-nine controls extending Level 1 with deeper monitoring, incident response, and assurance. Cyber Essentials Plus is the precondition at this tier and above.
Level 3
The highest tier, reserved for contracts carrying the most sensitive material. Scope, timeline, and assurance expectations are set contract by contract.
Cyber Essentials comes first
DCC is not a standalone certificate. Cyber Essentials is the precondition for Level 0 and Level 1, and Cyber Essentials Plus is the precondition for Level 2 and Level 3. Both must be current at the point of assessment.
- Cyber Essentials current within twelve months before DCC assessment
- Cyber Essentials Plus where the target level is 2 or above
- Scope of the certificate matched to the DCC organisational boundary
- Renewal cycle planned so certification does not lapse mid-assessment
Read the framework detail: Cyber Essentials, Cyber Essentials Plus, and Defence Cyber Certification.
Who this applies to
If your revenue touches the MOD supply chain, directly or through a prime, DCC reaches you.
Tier 2 and Tier 3 suppliers
Cyber requirements cascade down from Tier 1 primes through flowdown clauses. Most SMEs first meet DCC as a contractual condition, not as a choice.
Anyone holding a DEFCON 658 contract
DEFCON 658 requires a Cyber Security Risk Assessment and flowdown of the resulting risk level. DCC is the assurance layer sitting on top of that obligation.
Suppliers already profiled under Def Stan 05-138
The Def Stan 05-138 risk profile determines the DCC level in scope. Suppliers profiled Very Low or Low typically land at Level 0 or Level 1.
Background reading: DEFCON 658 and Def Stan 05-138.
How Goldline prepares you
Four steps from an unclear obligation to an evidence pack an assessor can work through.
Position and scope
Confirm the DCC level your contracts actually require, verify Cyber Essentials currency, and define the organisational boundary. Delivered as the DCC Level 0 Readiness Assessment.
Close the gaps
Remediate against the Def Stan 05-138 control set at the target level. Policy framework, asset inventory, risk methodology, and technical controls implemented to assessment standard.
Assemble the evidence
Build the evidence pack to submission standard and run an internal review against the assessment criteria, so nothing surfaces for the first time in front of an assessor.
Route to assessment
Introduce you to an IASME-accredited Certification Body and support the submission. Goldline prepares; the accredited body assesses and certifies.
Start here
DCC Level 0 Readiness Assessment
Level confirmation against your contracts, Cyber Essentials currency check, gap analysis against the Level 0 control set, and a costed route to assessment.
From £1,750 + VAT
Goldline is an implementation partner, not a Certification Body. DCC certificates are issued by IASME-accredited bodies, and scheme impartiality rules keep preparation and assessment separate. We introduce you to an accredited body at the right point.
Who delivers this
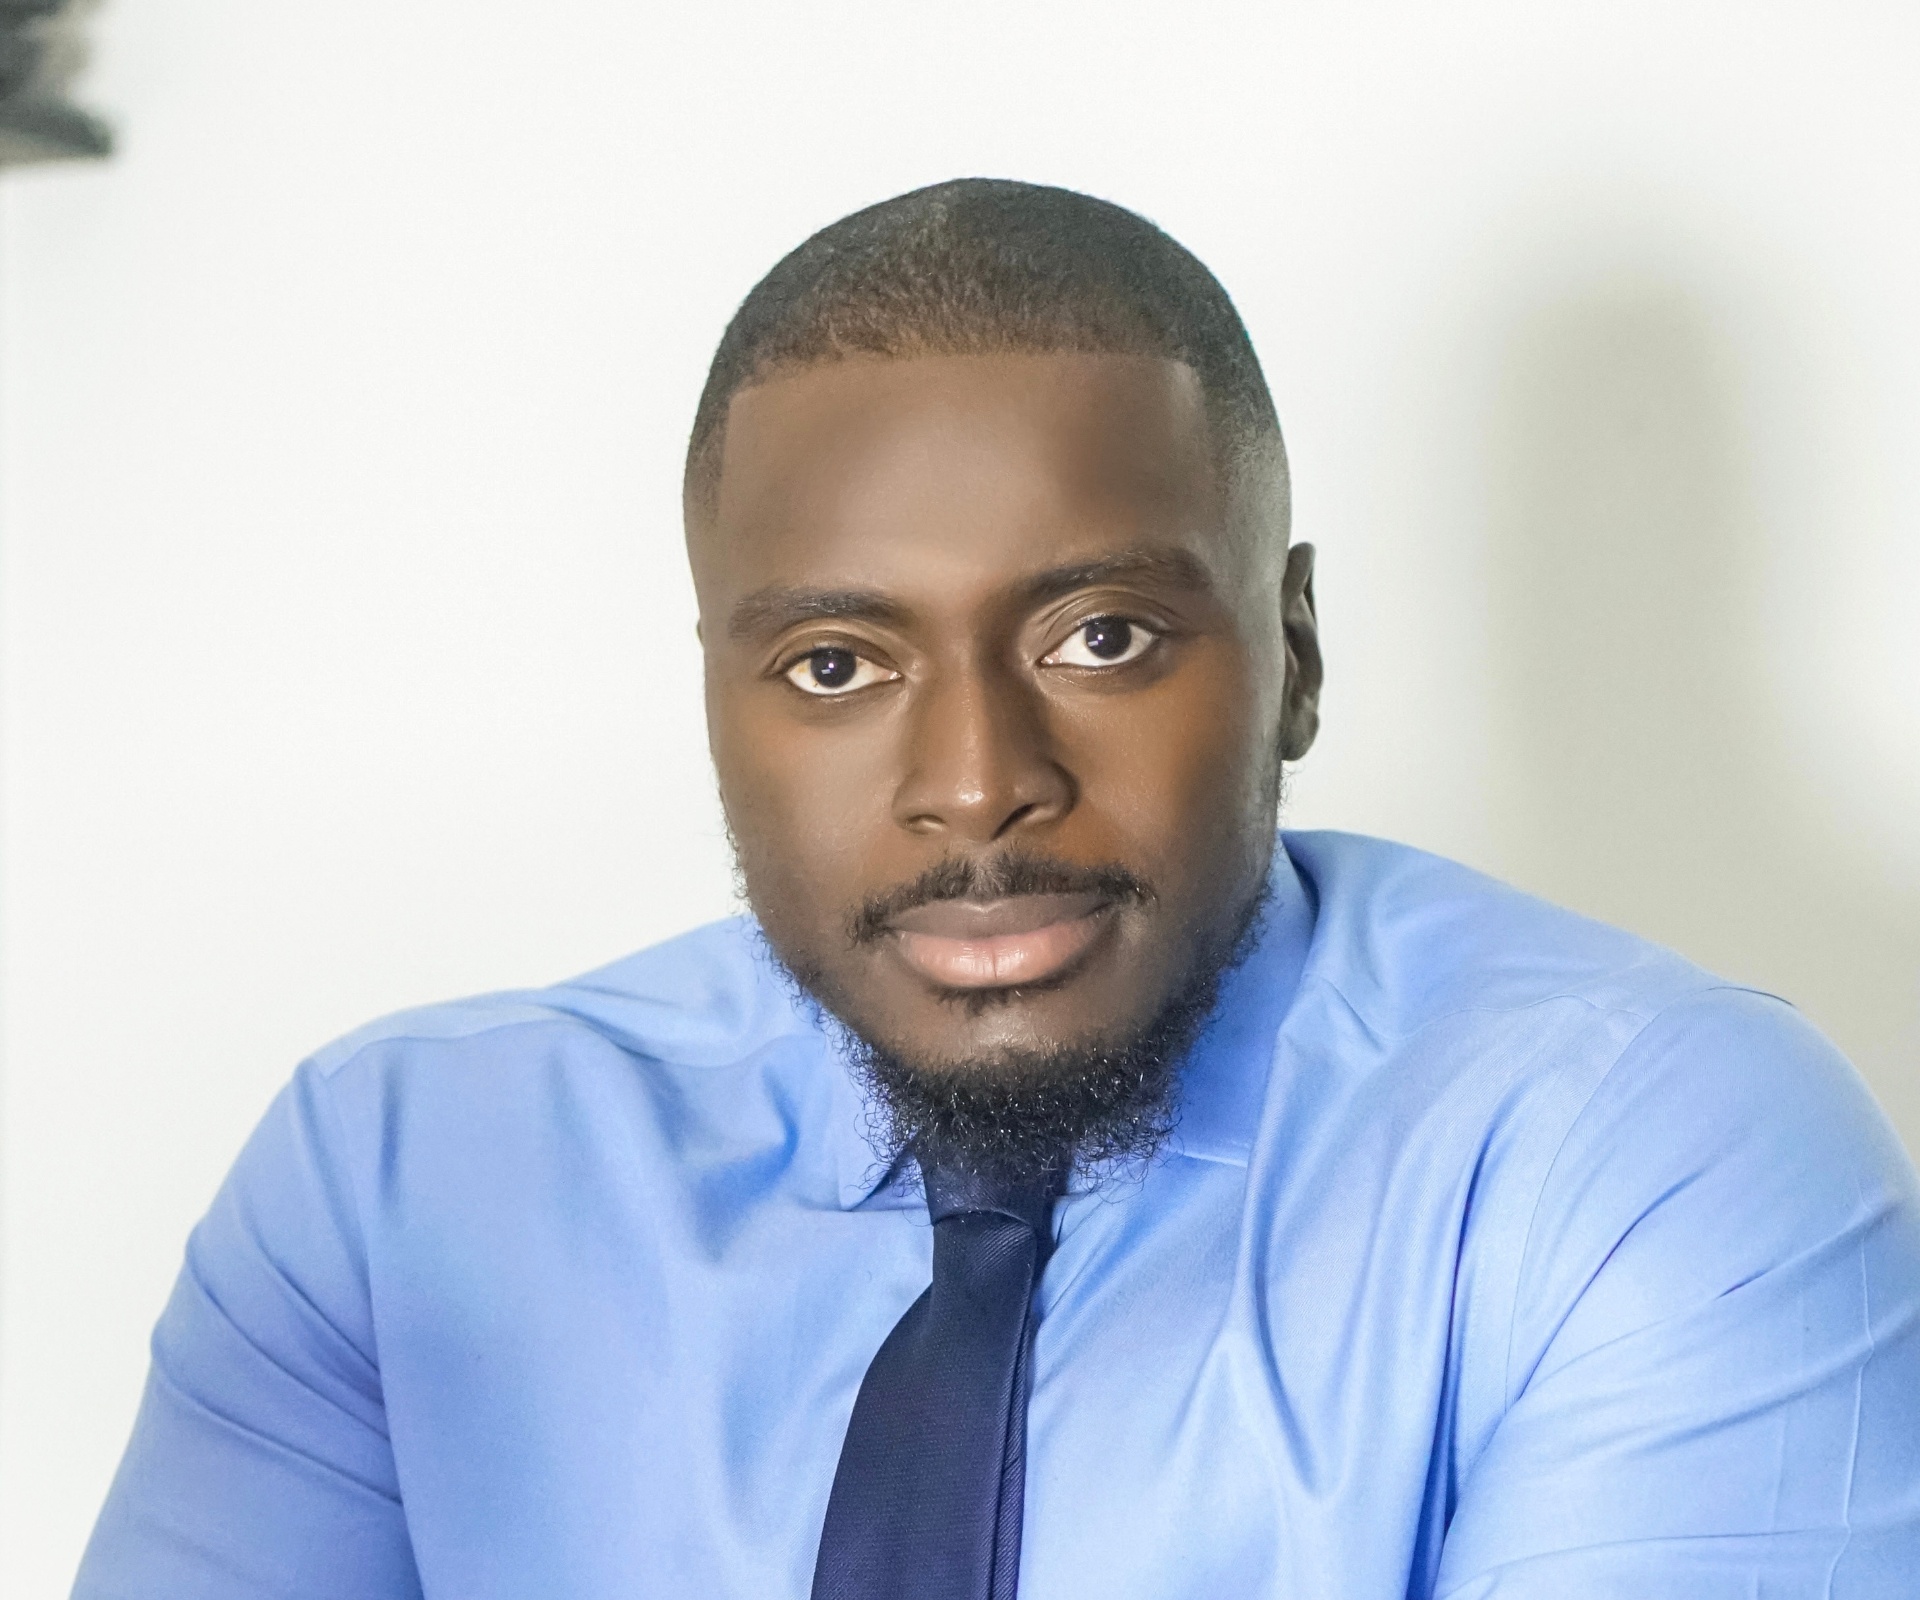
Alfred Obeng
Founder and Principal Consultant, Goldline Consultancy
Senior practitioner with thirteen years across UK Defence, Central Government, Automotive, Big Tech, and regulated industries. SC Cleared throughout delivery, with no junior delegation.
- ISO 42001 Lead Implementer (PECB)
- ISO 42001 Lead Auditor (PECB)
- ISO 27001 Senior Lead Implementer (PECB)
- ISO 27001 Lead Auditor (PECB)
- CISSP
Most defence SMEs pay twice for cyber compliance. Once for the consultancy, and again for the redaction overhead of working with a practitioner who cannot view the contract material. Clearance removes that at source.
Frequently asked
WHERE THIS STOPS
Goldline prepares you. An IASME-licensed Certification Body assesses you.
The Defence Cyber Certification assessment is carried out by an IASME-licensed Certification Body, not by Goldline. Goldline does the readiness work: the scope, the controls, the evidence and the gap closure that decide whether the assessment goes well. When the evidence is ready we introduce you to a Certification Body. DCC is a customer requirement set by the Ministry of Defence through its contracts. It is not a statutory obligation, and IASME's own guidance says it is not currently mandatory.
Book a scoping call
Thirty minutes to establish which DCC level your contracts require, where Cyber Essentials sits today, and what the route to 31 December 2026 looks like.
45 minutes, video, with the practitioner who would do the work. No sales pitch.