
ISO 42001 audit-ready for regulated UK organisations and AI-enabled scaleups.
For regulated UK organisations and AI-enabled UK scaleups where AI governance is now a procurement, investor, or regulatory question. Founder-led delivery. Fixed scope. The sequence is fixed. Your timeline is set at the free diagnostic. No junior delegation. The certification decision rests with your certification body.
Delivered by
Delivered on your GRC platform of choice, or ours.
45 minute call. No sales pitch. Senior practitioner-led discovery.
Loading the calendar
Open the booking pageCalendar not loading? Open Calendly directly
Background on the standard: ISO 42001 UK Consultant guide
info@goldlineconsultancy.co.ukMicrosoft now requires it from AI suppliers.
Under Microsoft's Supplier Data Protection Requirements, suppliers delivering AI systems must provide independent assurance against Section K of the DPR, either by completing an independent assessment against Section K or by submitting ISO 42001 certification.
Section K sets out the AI System obligations themselves, covering intended use disclosure, prohibited practices, responsible AI risk assessment, and an AI System incident response plan with rollback and feature disablement timings. These are the same artefacts an AI management system produces.
Source: Microsoft Supplier Data Protection Requirements v12, March 2026, and the SSPA Program Guide v12.
Microsoft is currently the only major enterprise publishing this requirement. Others have certified their own AI services without extending the requirement to suppliers.
The procurement context.
Five shifts that are moving ISO 42001 from "future consideration" to "named requirement" for regulated UK organisations and AI-enabled scaleups.
EU AI Act enforcement is active
Article 50 transparency obligations apply from 2 August 2026 and Annex III high-risk obligations from 2 December 2027. EU buyers already require demonstrable AI governance posture before procurement signature.
Enterprise questionnaires now ask
UK enterprise security questionnaires increasingly include AI governance questions alongside the standard ISO 27001 and SOC 2 controls.
US Fortune 500 acceptance
Buyers applying the NIST AI Risk Management Framework are accepting ISO 42001 as the equivalent international standard.
Investor diligence in 2026
AI governance maturity is now asked at the same point in the diligence process as security and privacy posture.
A shallow UK practitioner pool
Delivered by a practitioner holding both the ISO 42001 Lead Implementer and ISO 42001 Lead Auditor credentials from PECB. The UK pool credentialled to deliver this standard is small.
EU AI Act enforcement deadlines
The regulation phases enforcement across several years. ISO 42001 is the most direct international standard for demonstrating governance posture against EU AI Act risk-tier obligations.
| EU AI Act deadline | What applies |
|---|---|
| February 2025 | Prohibited AI practices and AI literacy |
| 2 August 2025 | General-purpose AI models and governance framework |
| 2 August 2026 | Article 50 transparency obligations, except Article 50(2) |
| 2 December 2026 | Article 50(2) for legacy systems and new prohibited practices |
| 2 August 2027 | National AI regulatory sandboxes established |
| 2 December 2027 | High-risk obligations for Annex III standalone systems |
| 2 August 2028 | High-risk obligations for Annex I embedded systems |
ISO 42001 covers approximately 40 to 50 percent of EU AI Act requirements through its AIMS framework, addressing core governance themes: risk management, transparency, human oversight, accuracy, and security controls. ISO 42001 is not a substitute for full EU AI Act compliance, but it is the most efficient management system foundation for the obligations EU enforcement is now bringing forward.
Two ways to approach ISO 42001.
Both can reach the same standard. They diverge on timeline, depth, and audit-defence readiness.
Manual or generalist approach
- Six months or more to certification readiness
- Templated policy documentation without AI-specific control depth
- Generic consultant unfamiliar with ISO 42001 specifics
- DIY platform implementation with no senior practitioner judgement
- Audit preparation discovered to be inadequate at Stage 1
With Goldline
- Structured delivery with senior practitioner accountability
- ISO 42001 Lead Implementer and Lead Auditor-led methodology, 19 activities mapped to AIMS lifecycle
- GRC platform integration with cross-mapped controls and AI-specific risk automation
- Founder-led senior practitioner delivery throughout
- Audit-defence readiness validated before Stage 1 submission
Four reasons buyers choose Goldline for ISO 42001.
ISO 42001 Lead Implementer and Lead Auditor credentials
Alfred Obeng holds the PECB ISO 42001 Lead Implementer and PECB ISO 42001 Lead Auditor credentials. Holding both implementation and audit credentials for ISO 42001 is a combination the UK market currently has very few of.
Dual ISO 27001 and ISO 42001 capability
Senior practitioner-led delivery across both standards inside one engagement. The cross-mapping work that lets ISO 27001 controls accelerate the AIMS implementation requires practitioner judgement in both frameworks, which is rare in the UK consultancy market.
Platform-operationalised AI automation
AI-specific risk automation (model drift, bias, explainability), cross-mapped controls between ISO 27001 and ISO 42001, and buyer-facing trust signalling, configured on your GRC platform of choice, or ours. The platform operationalises the evidence the senior practitioner designs.
Founder-led senior delivery
No subcontracted hours. No offshored work. No associate handoff. The practitioner who scopes the engagement is the practitioner who delivers it, from diagnostic call to certification audit.
19 activities. 4 phases. One structured methodology.
Senior practitioner delivery against the ISO 42001 AIMS lifecycle. Sequenced across the programme, with the timeline calibrated at scoping.
Typical blocker: AI use across the organisation has never been formally inventoried. Risk classification is informal. Without a documented AIMS scope, every subsequent phase is built on unstable ground.
How Goldline helps
Senior practitioner-led scope definition and AIMS boundary work. Governance committee established. AI inventory completed with EU AI Act risk classification. Risk assessment methodology agreed at organisational level.
What happens
- Activity 01. Scope definition and AIMS boundary. Establish framework boundaries and context.
- Activity 02. Stakeholder identification and governance committee. Identify key players and establish governance.
- Activity 03. Policy framework and management commitment. Develop overarching policies and secure buy-in.
- Activity 04. AI inventory and EU AI Act risk classification. Catalogue AI systems and categorise risk levels.
- Activity 05. Risk assessment methodology and treatment planning. Define risk criteria and mitigating actions.
Programme components.
Fixed price. Fixed scope. Senior practitioner-led from first conversation to audit.
ISO 42001 AIMS implementation
Across the four AIMS lifecycle phases. Senior practitioner-led throughout.
AI inventory and risk classification
Aligned to EU AI Act risk tiers and your operating context.
AI-specific risk tracking
Model drift, bias, explainability, robustness monitored in-platform.
Cross-mapping to ISO 27001
Reused controls surfaced and evidenced (ISO 27001 path tier).
AI Vendor Risk Management
Third-party AI risk operationalised through the platform's third-party risk module.
AI policy suite and documentation
Tailored AI policy, supporting procedures, role-based responsibilities.
Trust centre configured
Buyer-facing AI governance signalling, configured to your brand.
ISO 42001 audit readiness
Stage 1 and Stage 2 preparation with UKAS-accredited CB pathways.
Certification body audit fees are billed separately and pass through at cost. GRC platform subscriptions are billed separately; where Goldline supplies the platform as a partner, the price is confirmed in writing before purchase and you are free to buy direct instead.
Two delivery paths.
Tier selection depends on whether ISO 27001 is in place. Both tiers deliver to the ISO 42001 audit-ready milestone. The certification decision rests with your certification body. Investment shared at qualified discovery.
ISO 42001 Sprint - ISO 27001 Path
Timeline: calibrated at scoping
Best fit
Already ISO 27001 certified or in active implementation.
Why this tier
Substantial control reuse from your existing ISMS via cross-mapped platform controls. The AI overlay is faster when the security baseline is in place.
- Reuses existing ISO 27001 controls where applicable
- AI-specific controls layered on top
- Accelerated delivery via existing ISMS reuse
Pre-requisites
- ISO 27001 certified OR currently in active implementation
- One to five AI systems in scope
- Engineering team able to support evidence collection
ISO 42001 Sprint - Standalone
Timeline: calibrated at scoping
Best fit
No existing ISO 27001 implementation.
Why this tier
Full AIMS implementation from scratch including foundational governance scaffolding.
- Full AIMS implementation from scratch
- Foundational governance scaffolding included
- Full AIMS scaffolding delivery
The platform layer
Goldline delivers on your GRC platform of choice, or ours. The platform operationalises evidence collection, control automation, AI-specific risk tracking, and buyer-facing signalling. Platform selection is confirmed at scoping. Goldline remains the senior practitioner delivery layer throughout.
- Native ISO 42001 framework module with structured AIMS controls
- AI-specific risk automation: model drift, bias monitoring, explainability records
- Buyer-facing trust page for AI governance signalling
- Third-party risk module for AI vendor risk management
- Cross-mapped controls between ISO 27001 and ISO 42001 (ISO 27001 path tier)
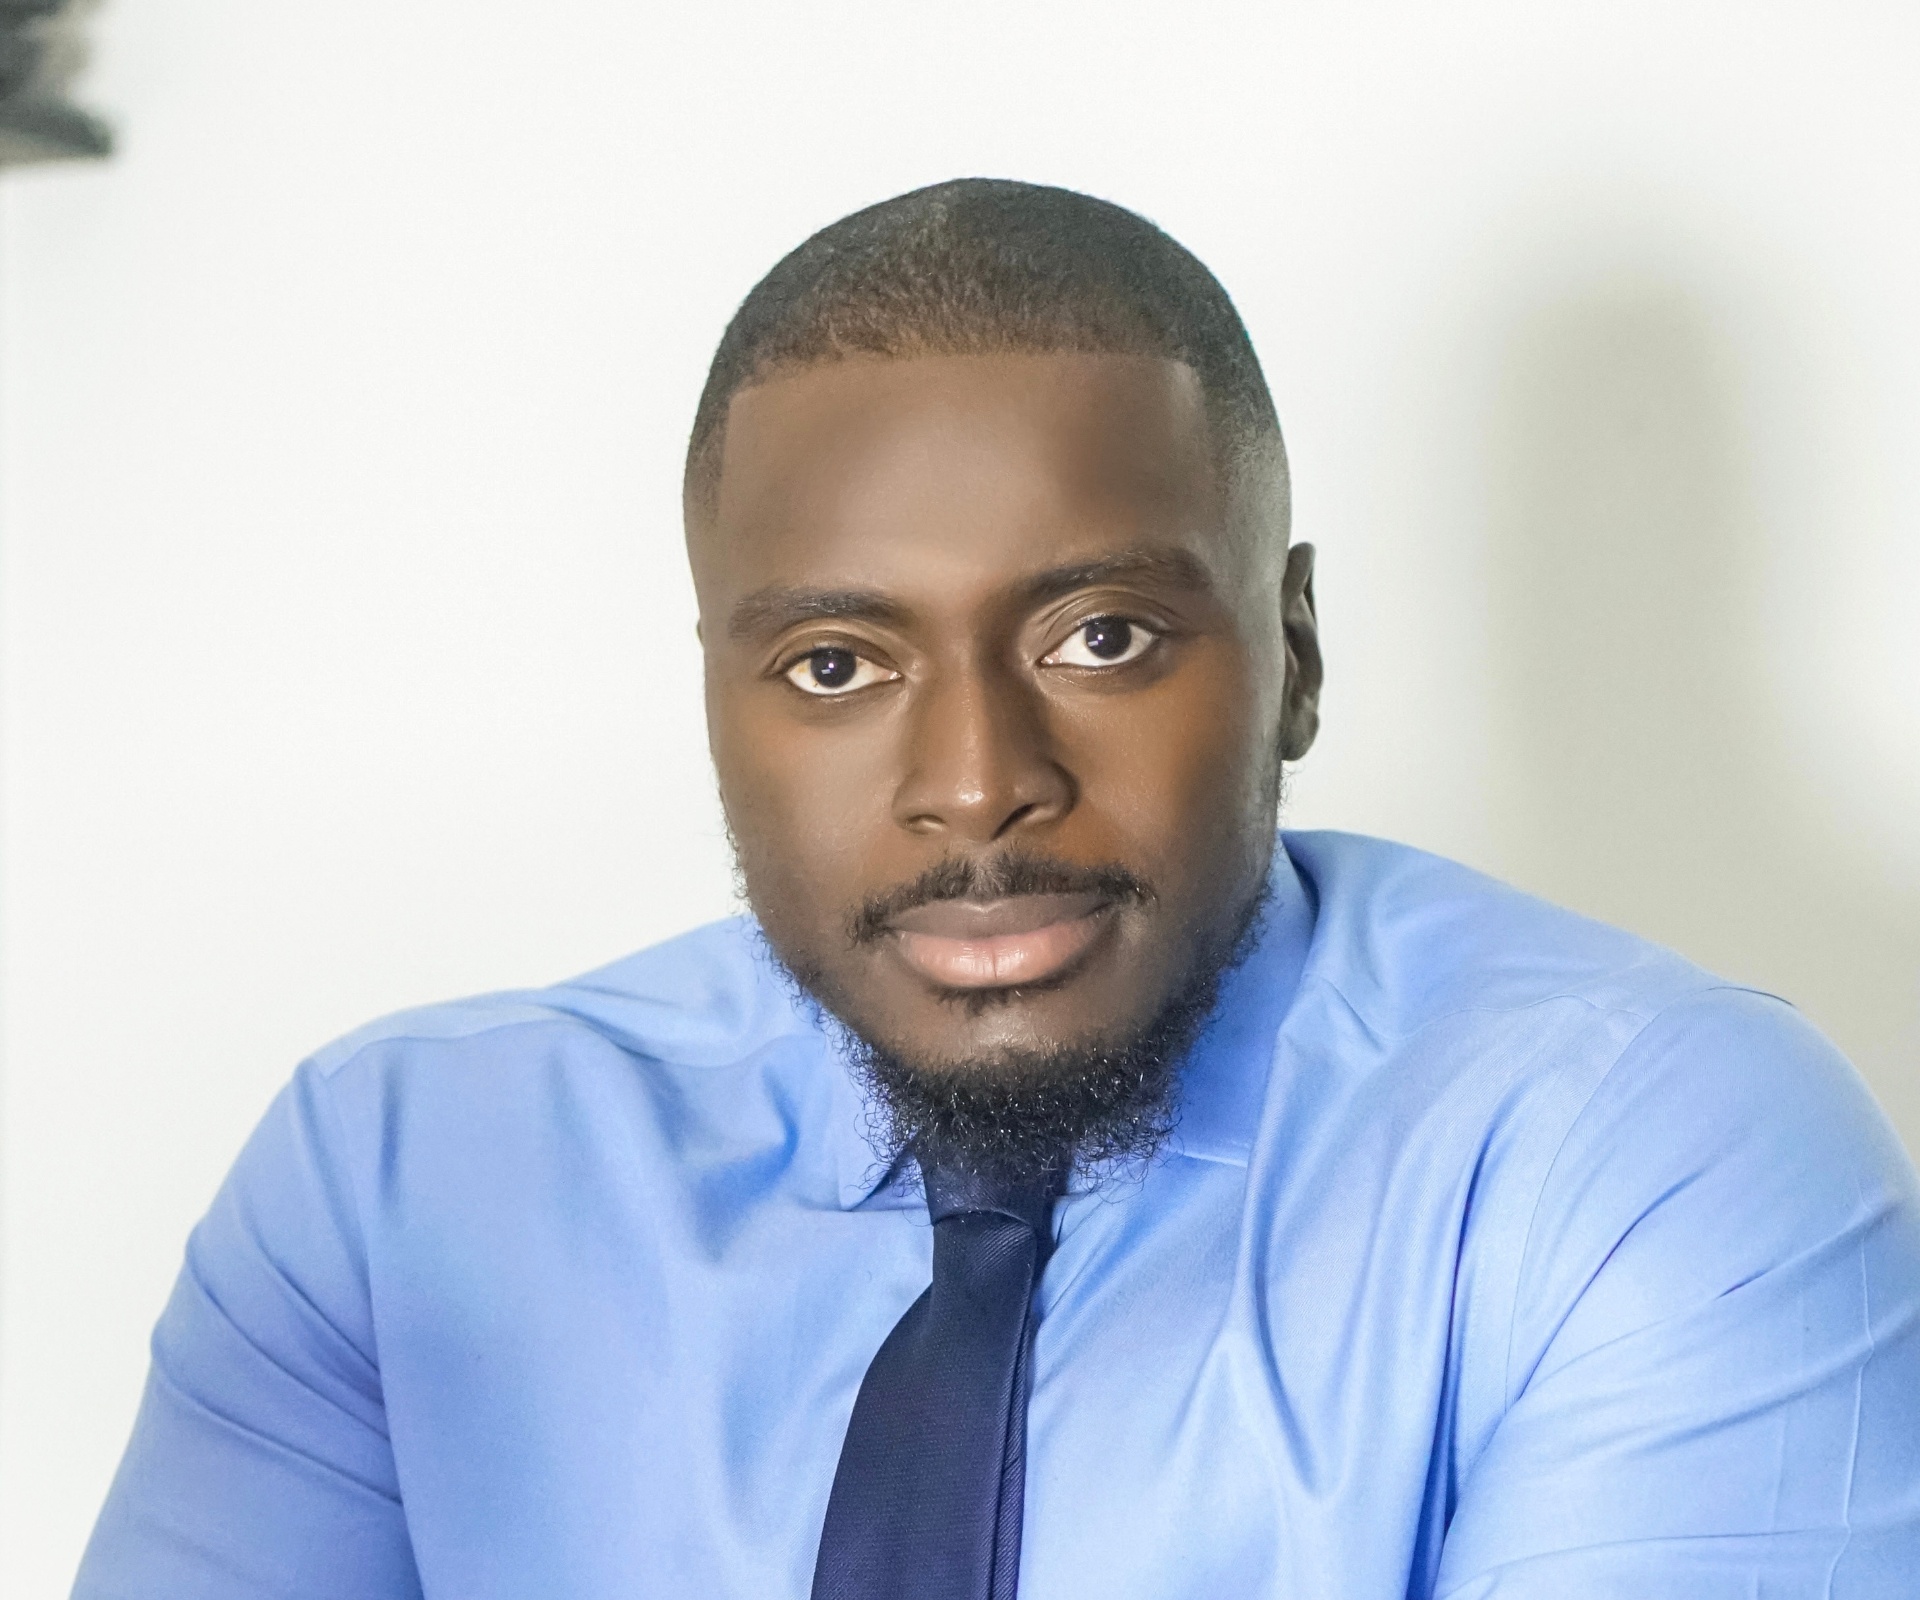
Alfred Obeng
Founder and senior practitioner. ISO 42001 Sprint engagements are delivered by the practitioner who scopes them, from the diagnostic call through to the certification audit. Currently completing an Executive MBA with AI specialism at the University of Hertfordshire (December 2026).
- ISO 42001 Lead Implementer and Lead Auditor (PECB)
- ISO 27001 Senior Lead Implementer and Lead Auditor (PECB)
- CISSP
- PMP
Why this delivery model exists
AI governance is increasingly asked by buyers on the same call as ISO 27001 and SOC 2. Treating ISO 42001 as a documentation exercise fails Stage 2. The ISO 42001 Sprint inverts that: senior practitioner designs the AIMS, the platform operationalises the evidence, certification audit follows.
From the first conversation to the audit report, the practitioner you meet is the practitioner doing the work.
Questions buyers ask before scoping.
Timeline depends on three factors: whether ISO 27001 is already in place, the number of AI systems in scope, and your engineering team's capacity to support evidence collection. Where ISO 27001 is certified, the AIMS layer can be implemented in a materially shorter window because controls and evidence reuse substantially. Where ISO 42001 is being implemented from scratch, the AIMS scaffolding takes longer to stand up. Specific timeline is calibrated at qualified discovery, not stated as a fixed week count, because misrepresenting timeline is the most common reason ISO 42001 programmes fail Stage 2 audit.
Background reading: ISO 42001 UK Consultant: what to look for and why the credential matters.
Are you ready for an accelerated ISO 42001 Sprint?
Five conditions that materially affect timeline and outcome. The closer your starting position to all five, the faster delivery runs and the more confident the Stage 2 outcome.
AI systems in production or active development
Your product or operations embed AI in customer-facing or decisioning workflows: generation, classification, recommendation, or model-served processing. The AIMS scopes around these systems. Suited to regulated organisations, financial services, healthcare, defence supply chain, and AI-enabled scaleups. Not calibrated for pre-revenue startups.
Existing information security foundation
ISO 27001, SOC 2, or equivalent in place or in active implementation accelerates the engagement materially. Control reuse and existing evidence reduce the AIMS scaffolding required.
Management commitment to AI governance
Designated AI governance contact, executive sponsor, and resourced engineering, data science, and security collaboration. AIMS depends on cross-functional accountability.
GRC platform readiness
Modern engineering stack compatible with leading GRC platform integrations, or willingness to onboard. Platform selection is confirmed at scoping.
AI risk awareness
Documented AI use cases, preliminary view on EU AI Act risk classification, identified AI-specific risks across bias, robustness, data quality, and explainability.
Maximise your compliance investment.
ISO 42001 is rarely the only framework an enterprise buyer asks for. The Goldline programme ladder lets you add adjacent certifications without rebuilding the management system.
Add ISO 27001 to your AIMS foundation
If you have taken ISO 42001 Sprint without an existing ISMS, ISO 27001 is typically the next logical layer. The AIMS controls you implemented substantially reuse into a full information security management system.
Discuss in discovery →Continuous compliance retainer
Continuous compliance, trust page managed service, security questionnaire automation, surveillance audit support. For organisations whose enterprise pipeline justifies a permanent operational compliance layer.
Discuss in discovery →Add sector-specific standards
PCI DSS, ISO 27017 and ISO 27018 (cloud), ISO 27701 (privacy), DCC for defence supply chain. Discuss in discovery.
Discuss in discovery →Representative delivery experience across government, defence and regulated industry.
Book a 45 minute strategy call.
Discuss your AI inventory, EU AI Act exposure, and which tier fits your timeline. 45 minute call. No sales pitch. Senior practitioner-led discovery.
Or email Alfred directly: alfred@goldlineconsultancy.co.uk