
ISO 27001 audit-ready. Fixed scope, timeline agreed at scoping. Built for regulated UK organisations and AI-enabled scaleups.
For regulated UK organisations, mid-market operators, and AI-enabled scaleups where enterprise procurement or supervisory review has surfaced ISO 27001 as the gate. Founder-led delivery. Fixed scope. The sequence is fixed. Your timeline is set at the free diagnostic. The certification decision rests with your certification body.
If you have engineers and a named internal owner with time, ISO 27001 Guided delivers the same management system for £7,000 + VAT.
Delivered by
Delivered on your GRC platform of choice, or ours.
Senior practitioner-led from first conversation to audit. free 45 minute diagnostic. No commitment.
Loading the calendar
Open the booking pageCalendar not loading? Open Calendly directly
Already certified somewhere? We can support an in-flight programme. Email Alfred
info@goldlineconsultancy.co.ukWhy ISO 27001 is now the deal gate.
Five shifts that moved ISO 27001 from preferred to required in UK enterprise sales cycles for regulated organisations and AI-enabled scaleups between 2024 and 2026.
60% of enterprise buyers now mandate it
In 2026, approximately 60% of enterprise buyers require ISO 27001 or equivalent before contract signature. For regulated UK organisations and AI-enabled scaleups selling into UK and EU enterprises, the certificate has shifted from optional differentiator to procurement checkbox.
Security questionnaire burden is exploding
Organisations selling into enterprise procurement now receive a median of 24 security questionnaires per quarter, up from 8 in 2022 (TrustMind survey of 142 security leaders). Each takes approximately 9.4 hours of staff time. That is around 225 hours per quarter, typically absorbed by the security lead or first dedicated hire.
Procurement slowdowns of two to four months
Without certification, enterprise security review adds four to twelve weeks of friction to every deal. Average procurement slowdowns of two to four months. For an organisation with a 90-day sales cycle, eliminating that friction is two months of revenue throughput per deal.
EU buyers expect it as baseline
Germany, the Netherlands, and the Nordics list ISO 27001 alongside GDPR as a baseline procurement requirement. NIS2 references ISO 27001 for Article 21 risk management. EU buyers no longer ask if you have it. They ask for the certificate.
The UK is moving in the same direction
The UK Cyber Security and Resilience Bill, expected to progress through 2026, aligns with ISO 27001 controls. UK regulated supply chain customers are already moving ahead of statutory deadlines. The procurement gate is hardening, not softening.
The certificate is the difference between deals that close in weeks and deals that stall in security review for months.
Fixed scope. Timeline calibrated at scoping.
Three phases. Senior practitioner delivery throughout. No platform-led shortcuts. The sequence is fixed. Your timeline is set at the free diagnostic. The certification decision rests with your certification body.
Scope and design
Senior practitioner identifies ISO 27001 scope, Statement of Applicability, and control gaps against the audit framework. Risk assessment methodology agreed at organisational level.
- ISMS scope and Statement of Applicability locked
- Gap analysis against ISO 27001:2022 Annex A
- Risk assessment methodology and treatment plan agreed
- GRC platform configured
- Policy framework drafted to audit standard
Implement and evidence
Controls deployed across the in-scope environment. Evidence collection automated through the GRC platform. Pre-audit remediation completed. Internal audit conducted prior to certification body engagement.
- All in-scope controls implemented
- Evidence collection live in the GRC platform
- Policy framework deployed
- Pre-audit remediation completed
- Internal audit complete
Audit-ready and certify
Pre-audit readiness review. UKAS-accredited certification body engagement coordinated. Stage 1 audit completed at the agreed point in the programme. Stage 2 audit scheduled.
- Pre-audit readiness validated
- UKAS-accredited certification body engagement coordinated
- ISO 27001 Stage 1 readiness audit completed
- Stage 2 certification audit scheduled
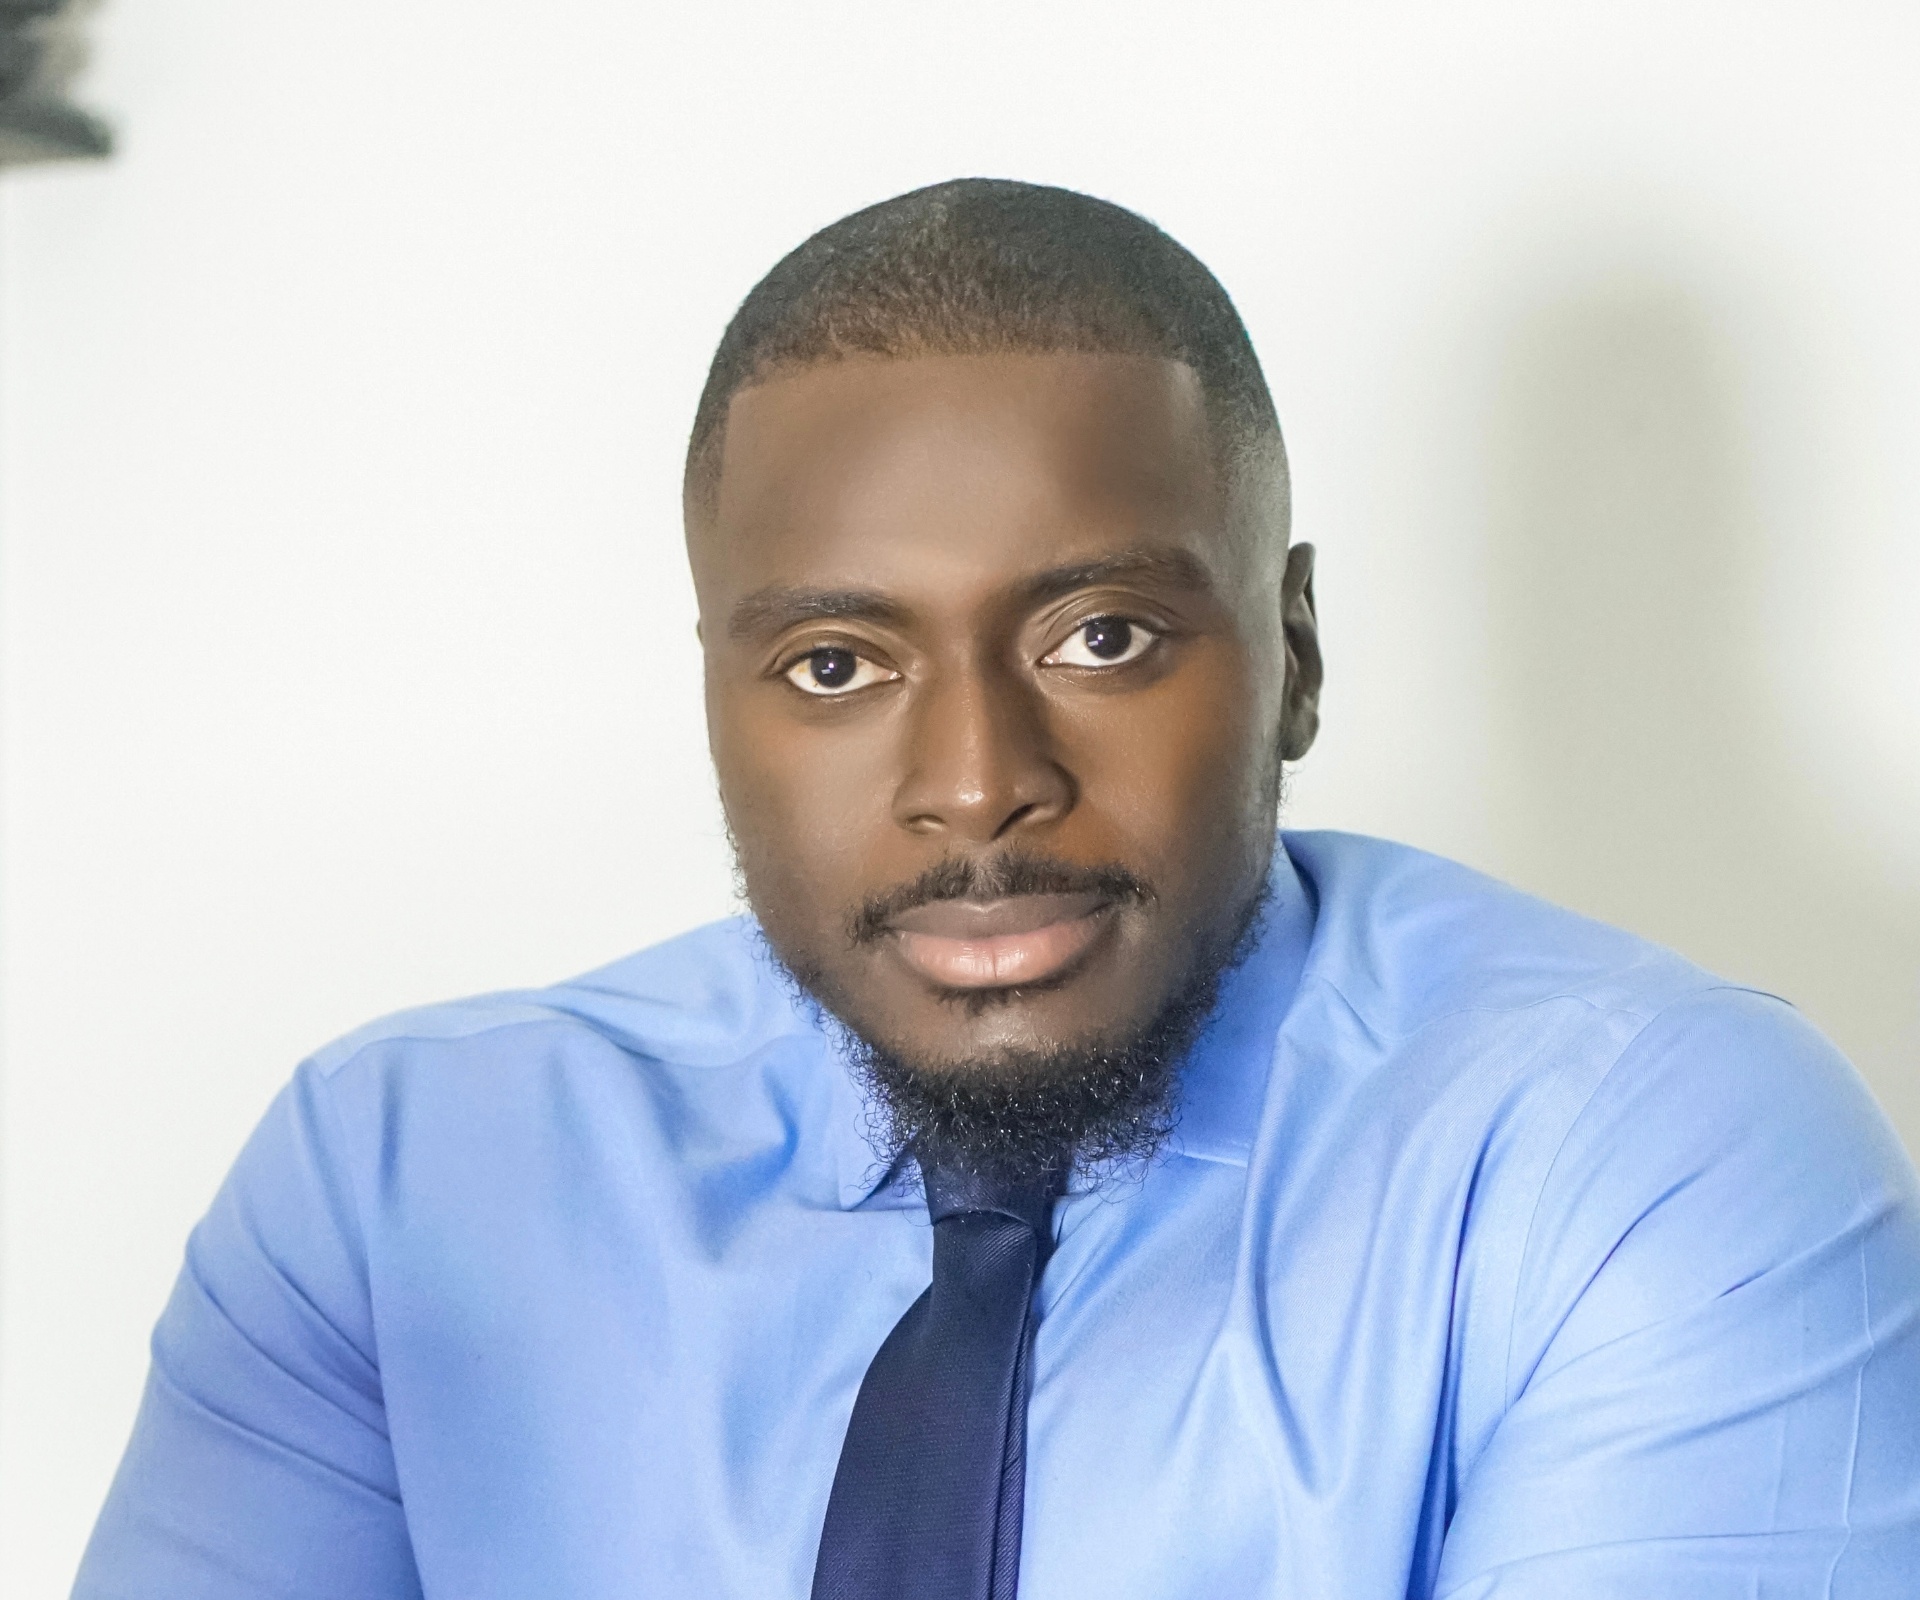
Alfred Obeng
Founder and senior practitioner. ISO 27001 Sprint engagements are delivered by the practitioner who scopes them, from the diagnostic call through to the certification audit. Thirteen years across UK Defence, Central Government, Automotive, Big Tech and Regulated Industries, and currently reading an Executive MBA with AI specialism at the University of Hertfordshire.
- ISO 42001 Lead Implementer and Lead Auditor (PECB)
- ISO 27001 Senior Lead Implementer and Lead Auditor (PECB)
- CISSP
- PMP
Why this delivery model exists
Most regulated UK organisations and AI-enabled scaleups buy a GRC platform and discover later that a platform is not a management system. The ISO 27001 Sprint inverts that sequence. Senior practitioner designs the management system. The GRC platform operationalises the evidence. Audit follows.
From the first conversation to the audit report, the practitioner you meet is the practitioner doing the work.
What the ISO 27001 Sprint includes.
Fixed scope. No hidden professional service overrun.
ISMS scope and Statement of Applicability
Senior practitioner-defined scope tailored to your operating environment.
Gap analysis against ISO 27001:2022 Annex A
Full Annex A control mapping with remediation roadmap.
Risk assessment and treatment plan
Risk methodology agreed at organisational level. Treatment plan operationalised.
Policy framework drafted to audit standard
Tailored to your operating environment. Not a template library.
GRC platform fully configured
All integrations live, evidence automation operational, ISO 27001 framework module deployed.
Internal audit and management review
Audit-grade evidence prepared before certification body engagement.
ISO 27001 Stage 1 readiness audit completed within the Sprint window
Pre-audit readiness validated. UKAS-accredited certification body engagement coordinated.
Stage 2 audit coordination
Certification body scheduling and Stage 2 audit support included.
Certification body audit fees are billed separately and pass through at cost. GRC platform subscriptions are billed separately; where Goldline supplies the platform as a partner, the price is confirmed in writing before purchase and you are free to buy direct instead.
THE CHOICE
What you are actually choosing between
| A consultant | A platform on its own | Goldline | |
|---|---|---|---|
| Who does the work | Someone senior, billed by the day | Your team, guided by the software | The practitioner who scoped it, on a fixed scope |
| What you get | Advice, and documents you then implement | Evidence collection and continuous control monitoring | The management system, and the evidence to prove it operates |
| Scope and Statement of Applicability | Usually included | Not produced. It records decisions only you can take | Written and defended at audit |
| Clause 9.2 internal audit | Only if independent of the build | Not performed. Software cannot audit itself | Delivered independently, or an independent auditor introduced |
| Your team's time | Meetings, then the work lands with you | Substantial. The platform tracks tasks, it does not do them | A few hours a week during delivery |
| In the room at Stage 2 | Depends on the engagement | No | Yes |
| Commercial shape | Day rate, open ended | Annual licence | Fixed scope, fixed fee, agreed before work starts |
A consultant
- Who does the work
- Someone senior, billed by the day
- What you get
- Advice, and documents you then implement
- Scope and Statement of Applicability
- Usually included
- Clause 9.2 internal audit
- Only if independent of the build
- Your team's time
- Meetings, then the work lands with you
- In the room at Stage 2
- Depends on the engagement
- Commercial shape
- Day rate, open ended
A platform on its own
- Who does the work
- Your team, guided by the software
- What you get
- Evidence collection and continuous control monitoring
- Scope and Statement of Applicability
- Not produced. It records decisions only you can take
- Clause 9.2 internal audit
- Not performed. Software cannot audit itself
- Your team's time
- Substantial. The platform tracks tasks, it does not do them
- In the room at Stage 2
- No
- Commercial shape
- Annual licence
Goldline
- Who does the work
- The practitioner who scoped it, on a fixed scope
- What you get
- The management system, and the evidence to prove it operates
- Scope and Statement of Applicability
- Written and defended at audit
- Clause 9.2 internal audit
- Delivered independently, or an independent auditor introduced
- Your team's time
- A few hours a week during delivery
- In the room at Stage 2
- Yes
- Commercial shape
- Fixed scope, fixed fee, agreed before work starts
Certification body audit fees are billed separately and pass through at cost.
TWO ROUTES
Two ways to get it done
| ISO 27001 Guided | ISO 27001 Sprint | |
|---|---|---|
| Who does the implementation | Your team, with direction | Goldline |
| What you need to have | Engineers, and a named internal owner with time | A decision maker and access |
| Your team's time each week | Several hours | A few hours |
| Scope and Statement of Applicability | Drafted with you | Written for you |
| Policy framework | Templates plus review | Written for your operating environment |
| Internal audit | Independent auditor introduced | Independent auditor introduced |
| Stage 2 attendance | Available | Included |
| Best for | A team that has the people and wants the method | A team whose people are building the product |
ISO 27001 Guided
- Who does the implementation
- Your team, with direction
- What you need to have
- Engineers, and a named internal owner with time
- Your team's time each week
- Several hours
- Scope and Statement of Applicability
- Drafted with you
- Policy framework
- Templates plus review
- Internal audit
- Independent auditor introduced
- Stage 2 attendance
- Available
- Best for
- A team that has the people and wants the method
ISO 27001 Sprint
- Who does the implementation
- Goldline
- What you need to have
- A decision maker and access
- Your team's time each week
- A few hours
- Scope and Statement of Applicability
- Written for you
- Policy framework
- Written for your operating environment
- Internal audit
- Independent auditor introduced
- Stage 2 attendance
- Included
- Best for
- A team whose people are building the product
When to choose ISO 27001 Guided: you have engineers and a named internal owner with the time, and you want to come out of it understanding the management system well enough to run it yourselves.
When to choose the ISO 27001 Sprint: your team is building the product and cannot carve the time out, and you would rather the work sat with the practitioner.
Both routes deliver the same management system. The difference is who does the work and how much of your week it costs.
Questions buyers ask before scoping.
Typically yes, with conditions: scope locked at kickoff, senior practitioner delivery throughout with no junior handoffs, and the GRC platform operating the evidence layer. The Sprint is scoped to reach the Stage 1 audit-ready milestone for a single entity, with the timeline calibrated at scoping rather than quoted as a fixed week count. Stage 2 schedules with the certification body thereafter, depending on the CB's calendar, and the certification decision rests with your certification body. The sequence is fixed. Your timeline is set at the free diagnostic.
Representative delivery experience across government, defence and regulated industry.
Book a 45 minute strategy call.
Discuss your ISO 27001 scope, UK and EU procurement pressure, and whether the Sprint fits your timeline. No sales pitch. No commitment.
No commitment to scope on the call. If the Sprint is not the right fit, we will tell you and recommend the alternative.
Or email Alfred directly: alfred@goldlineconsultancy.co.uk